Ikea and Zoom among websites hit by major security incident at third-party provider
Resumen detallado
Malicious JavaScript was aimed at visitors of websites belonging to 178 organisations across multiple sectors through third-party platform, Optimizely. The post Ikea and Zoom…
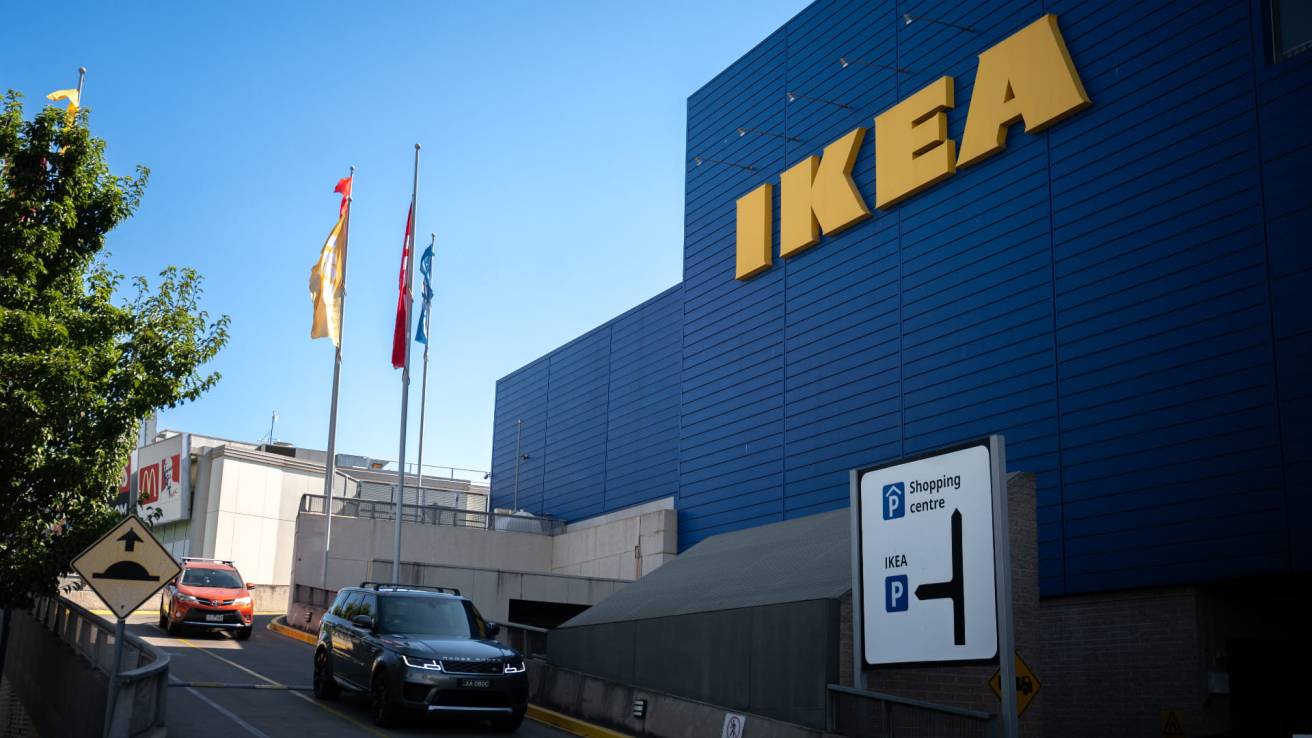
Some of the world’s most-visited websites, including those of Zoom, HSBC, Equifax, CNN, Salesforce and IKEA, have been compromised in an effort to steal cryptocurrency and infect iPhones.
Malicious JavaScript was aimed at visitors of websites belonging to 178 organisations across multiple sectors through Optimizely, a website optimisation platform, according to cybersecurity researcher Scott Helme.
Optimizely confirmed the incident and said it had identified “a security incident in which an unauthorised party exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects”.
According to Helme, the scripts attempted to replace cryptocurrency payment addresses with the attacker’s wallet.
By continuing, you agree to our Terms & Conditions and Privacy Policy.
Cybersecurity firm HudsonRock said it had also found evidence that the affected sites had served malicious code to visitors.
Optimizely said it had fixed the vulnerability, removed the injected code from affected projects, taken steps to secure affected user accounts and put additional protections in place to prevent unauthorised code from being delivered.
Reuters could not immediately determine whether the malicious code had been successfully used in each case or the extent of any resulting compromises.
Salesforce and IKEA said they were investigating the incident linked to Optimizely script changes. Salesforce said it had disabled scripts from the platform as a precaution.
Inicio del artículo, extracto de SmartCompany. Para leer el resto, abra el artículo en el sitio del medio.
MarketNews muestra el titular y el resumen publicados por el medio. El artículo completo se lee en el sitio del editor. (www.smartcompany.com.au)