Visa and Mastercard confirm customer data exposure following acyberattack on vendor
Resumen detallado
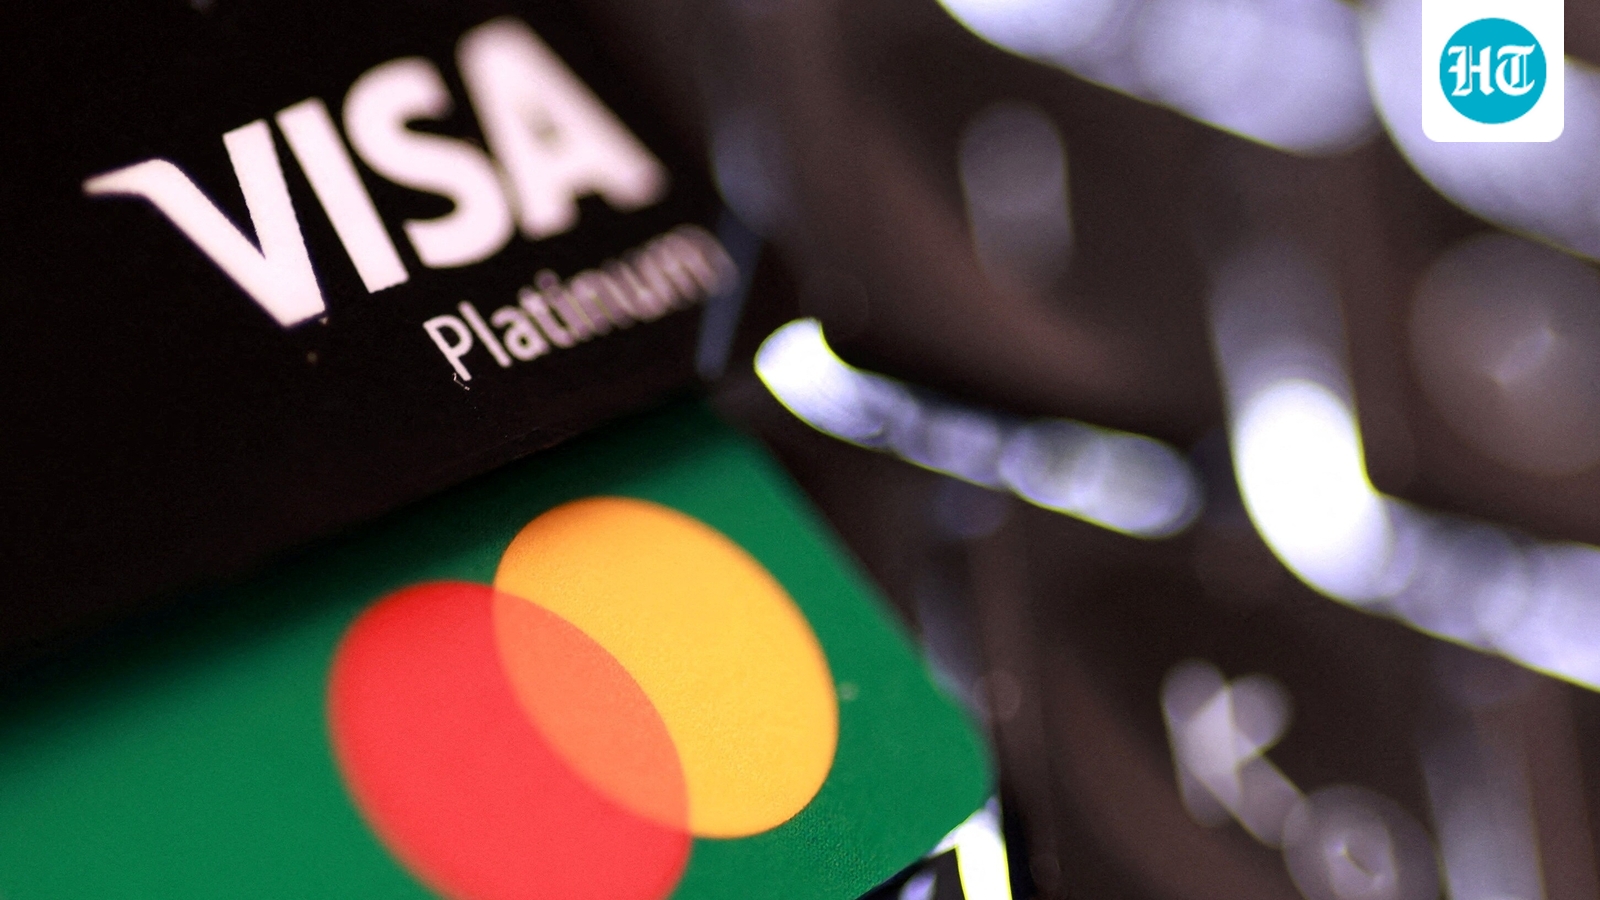
Visa and Mastercard confirm a third-party cyberattack exposed limited customer information, while both companies report no impact on their payment networks.
Visa and Mastercard have confirmed a cybersecurity incident involving a third-party service provider, with some customer information accessed in the attack. Both payment companies have stressed that their own systems and payment networks were not affected.
The incident involved a service provider in the Asia-Pacific region, according to Visa. Mastercard also confirmed that a limited amount of information belonging to some cardholders enrolled in a specific benefits programme was exposed.
The disclosures came on Thursday, November 19, after the ransomware group n0n claimed responsibility for the attack, according to The Wall Street Journal, citing cybersecurity firm SOCRadar. However, the companies have not identified the affected service provider or confirmed the full extent of the information accessed.
According to the report, which first reported details of the customer data leak, the incident also involved JPMorgan Chase. The bank separately confirmed that attackers may have accessed marketing information held by its third-party vendors.
Inicio del artículo, extracto de Hindustan Times. Para leer el resto, abra el artículo en el sitio del medio.
MarketNews muestra el titular y el resumen publicados por el medio. El artículo completo se lee en el sitio del editor. (www.hindustantimes.com)